CompTIA Security+ V8 vs. V7: What’s Changing in 2026?
- CompTIA Security+ V8 (SY0-801) is expected to launch November 17, 2026; the V7 (SY0-701) English exam retires June 11, 2027.
- V8 adds a dedicated objective on AI threats and vulnerabilities, including prompt injection, model poisoning and AI jailbreaking.
- Domain weighting shifts: General Security Concepts rises 12% to 16%, while Security Program Management and Oversight falls 20% to 14%.
- Exam length, question limit, passing score and three-year validity are unchanged.
- Both versions lead to the same Security+ certification, so there is no need to wait for V8 if you are already studying for V7.
Cybersecurity is constantly evolving, and the certifications that validate cybersecurity skills must evolve with it.
On November 17, 2026, CompTIA is expected to launch Security+ V8 (SY0-801), introducing updated exam objectives that reflect today’s changing threat landscape, emerging technologies, and modern security responsibilities.
While the foundational cybersecurity principles remain, V8 brings increased attention to artificial intelligence (AI), evolving attack techniques, and modern security operations.
So, what exactly is changing? And if you’re planning to earn your Security+ certification, should you take the current V7 exam or prepare for V8?
Here’s what you need to know.
When Does CompTIA Security+ V8 Launch?
The new CompTIA Security+ V8 (SY0-801) exam is scheduled to launch on November 17, 2026, replacing the current SY0-701 exam over a transition period.
Key dates to know:
- November 17, 2026: Expected Security+ V8 (SY0-801) launch
- June 11, 2027: Security+ V7 (SY0-701) English-language exam retirement
During this overlap, candidates will have the opportunity to choose which exam version best aligns with their training and certification timeline.
Importantly, both exam versions lead to the same CompTIA Security+ certification. Earning Security+ through the V7 exam does not make your certification less valuable or require you to retest when V8 launches.
What’s New in CompTIA Security+ V8?
The V8 update reflects how cybersecurity roles and responsibilities are changing. Although many foundational concepts carry forward from V7, several areas receive updated or more explicit coverage.
1. Artificial Intelligence Security Takes Center Stage
One of the most notable changes is the introduction of a dedicated exam objective focused on threats and vulnerabilities associated with AI usage.
As organizations integrate AI into everyday operations, cybersecurity professionals must understand the new risks these systems introduce.
Security+ V8 addresses topics such as:
- Prompt Injection: Attempts to manipulate AI systems through malicious or misleading instructions.
- Model Poisoning: Compromising the data or processes used to train AI models.
- Data Loss and Privacy: Risks involving sensitive information exposed through AI applications.
- AI Hallucinations: Inaccurate or fabricated AI-generated outputs that can create security and operational risks.
- AI Jailbreaking: Attempts to bypass an AI system’s intended restrictions or safeguards.
The update reflects a broader shift in cybersecurity: protecting an organization’s systems and data increasingly includes understanding the security implications of AI-enabled technologies.
Why Does This Matter?
As organizations adopt AI-powered tools, cybersecurity professionals must be prepared to identify risks that extend beyond traditional networks and applications. Understanding AI-related vulnerabilities helps security teams better protect sensitive data, assess emerging threats, and support responsible AI adoption.
2. Expanded Coverage of Emerging Cyber Threats
Cybercriminals continue to develop new methods of targeting organizations, employees, and critical infrastructure.
Security+ V8 explicitly addresses a range of contemporary attack techniques, including:
- Deepfake Attacks: AI-generated or manipulated audio and video used to impersonate trusted individuals.
- QR-Code Phishing (Quishing): Malicious QR codes designed to direct users to fraudulent websites or credential-harvesting pages.
- Fileless Malware: Malicious activity that operates without relying on traditional executable files.
- MFA Bypass: Techniques attackers use to circumvent multifactor authentication protections.
Understanding these techniques helps cybersecurity professionals identify suspicious activity, recognize potential vulnerabilities, and select appropriate defensive measures.
3. Updated Cloud and Enterprise Security Technologies
Modern organizations operate across cloud platforms, hybrid environments, remote endpoints, and interconnected applications.
Security+ V8 continues to emphasize securing these environments while incorporating updated technologies and practices, including:
- Cloud Security Posture Management (CSPM)
- Security Service Edge (SSE)
- Zero Trust architecture
- Identity and access management
- Secrets management and scanning
These concepts help cybersecurity professionals understand how to protect resources, manage access, and identify vulnerabilities across complex IT environments.
4. Continued Focus on Security Operations
Security operations remain the largest component of the Security+ exam.
V8 continues to emphasize critical operational responsibilities, including vulnerability management, security monitoring, incident response, access controls, and implementing appropriate security protections.
The updated objectives reflect the need for cybersecurity professionals who can do more than recognize security terminology. They must also understand how to apply security concepts in realistic situations.
Security+ V7 vs. V8: Exam Domain Comparison
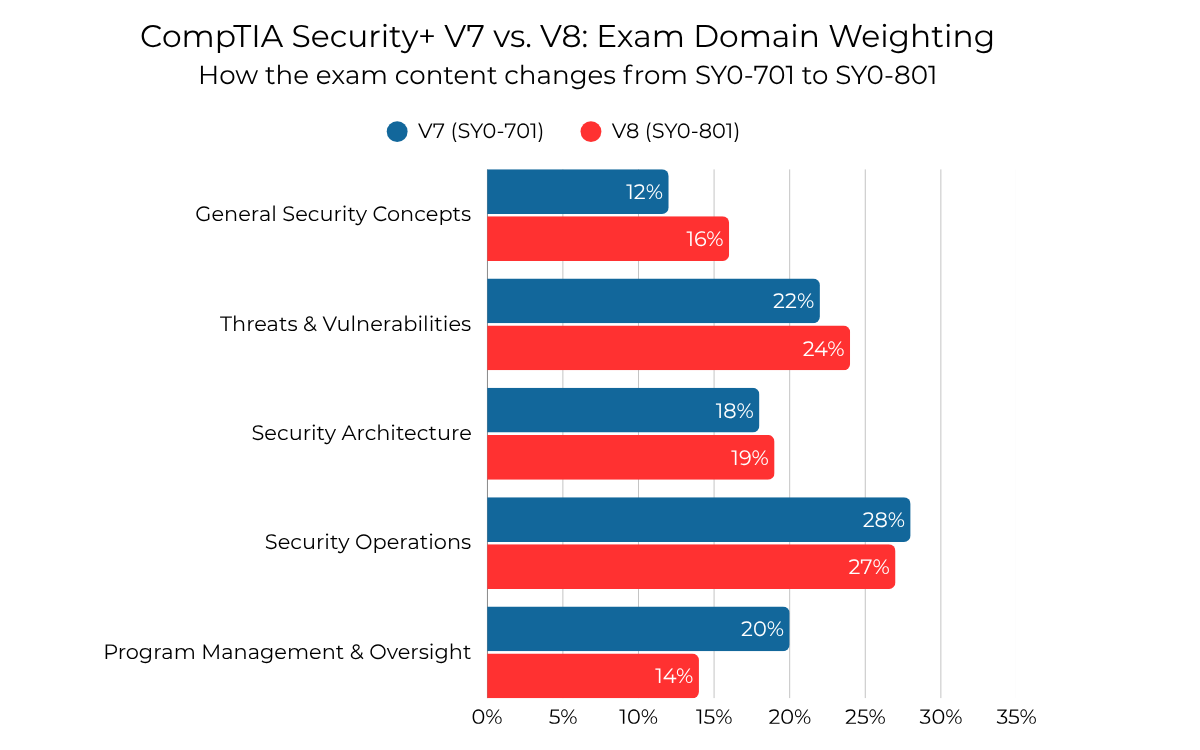
Both versions of Security+ organize their content into five major domains. However, V8 adjusts how much of the exam is dedicated to each area.
Several changes stand out:
- General Security Concepts increases from 12% to 16%, placing greater relative emphasis on foundational security principles.
- Threats, Vulnerabilities, and Attacks increases from 22% to 24%, reflecting continued attention to recognizing and understanding security threats.
- Security Operations remains the largest domain at 27%, underscoring the importance of practical cybersecurity responsibilities.
- Security Program Management and Oversight decreases from 20% to 14%. Governance, risk, and compliance remain part of the exam despite the reduced weighting.
These changes demonstrate that V8 is not an entirely new certification. Instead, it builds on established cybersecurity fundamentals while adjusting the content to better reflect current technologies and threats.
What Stays the Same in Security+ V8?
Although the exam objectives are changing, several important elements remain consistent.
Both V7 and V8 include:
- A maximum of 90 questions
- Multiple-choice and performance-based questions
- A 90-minute exam duration
- A passing score of 750 on a scale of 100–900
- A certification validity period of three years
Both versions also validate foundational cybersecurity knowledge applicable to a wide range of IT and security roles.
The primary difference is what candidates need to study, not the overall certification they earn.
Should You Take Security+ V7 or Wait for V8?
With two exam versions available during the transition, the right decision depends largely on your current preparation and certification timeline.
Choose Security+ V7 (SY0-701) If:
- You’ve already started studying using V7 materials.
- You’re planning to take the exam before June 11, 2027.
- You want to earn your certification without delaying your current training plans.
If you’re already preparing for SY0-701, there’s no reason to abandon your progress solely because a new version is launching.
Consider Security+ V8 (SY0-801) If:
- You’re beginning your cybersecurity certification journey.
- You want training aligned with the latest exam objectives.
- You’re interested in updated coverage of AI security and emerging cyber threats.
- Your training and exam timeline falls after the V8 launch.
The bottom line: You don’t need to wait for V8 to earn a valuable Security+ certification. Both versions lead to the same credential, so choose the exam that best fits your preparation and goals.
Prepare for Security+ V8 with Applied Technology Academy
Applied Technology Academy (ATA) is preparing to offer updated, instructor-led Security+ V8 training aligned with the new SY0-801 exam objectives.
Our V8 courses will feature updated courseware and hands-on labs to help students build practical cybersecurity skills while preparing for certification.
Upcoming Security+ V8 Instructor-Led Training
- November 30 – December 10, 2026: Evening Class
- December 14–18, 2026: Daytime Class
- January 25–29, 2027: Daytime Class
Whether you’re balancing training with a full-time job, preparing for a cybersecurity career, or developing your organization’s security capabilities, ATA offers instructor-led training options to fit your schedule.
Ready to prepare for Security+ V8? Explore Security+ Training →
Stay Ahead of What’s Next in Cybersecurity
Cybersecurity professionals must continually adapt as technologies, vulnerabilities, and attack methods evolve.
CompTIA Security+ V8 reflects this changing environment by building on foundational security skills while introducing updated coverage of AI-related risks, modern threats, and enterprise security practices.
Whether you choose V7 or V8, building a strong cybersecurity foundation is an important step toward advancing your IT security knowledge and career.
Frequently asked questions
Is Security+ V8 harder than V7?
Not necessarily. V8 includes updated exam objectives and more explicit coverage of certain emerging threats, but the exam duration, question limit and passing score remain the same. Difficulty will depend on your experience and preparation.
Will Security+ V7 still be valid after V8 launches?
Yes. Earning Security+ through SY0-701 results in the same certification. Existing certifications remain valid according to CompTIA's normal renewal requirements.
When does Security+ SY0-701 retire?
The English-language SY0-701 exam is scheduled to retire June 11, 2027.
Does Security+ V8 include artificial intelligence?
Yes. V8 includes a dedicated objective addressing AI-related threats and vulnerabilities, including prompt injection, model poisoning, data loss and AI hallucinations.
Do I need to retake Security+ if I already passed V7?
No. CompTIA does not require existing Security+ certification holders to retake the exam whenever a new version is introduced. Standard certification renewal requirements still apply.